Technical Expertise
Over 23 years of dedicated experience in securing and hardening enterprise infrastructure across diverse platforms and environments
Mark Darland
Infrastructure Security Specialist
Resume
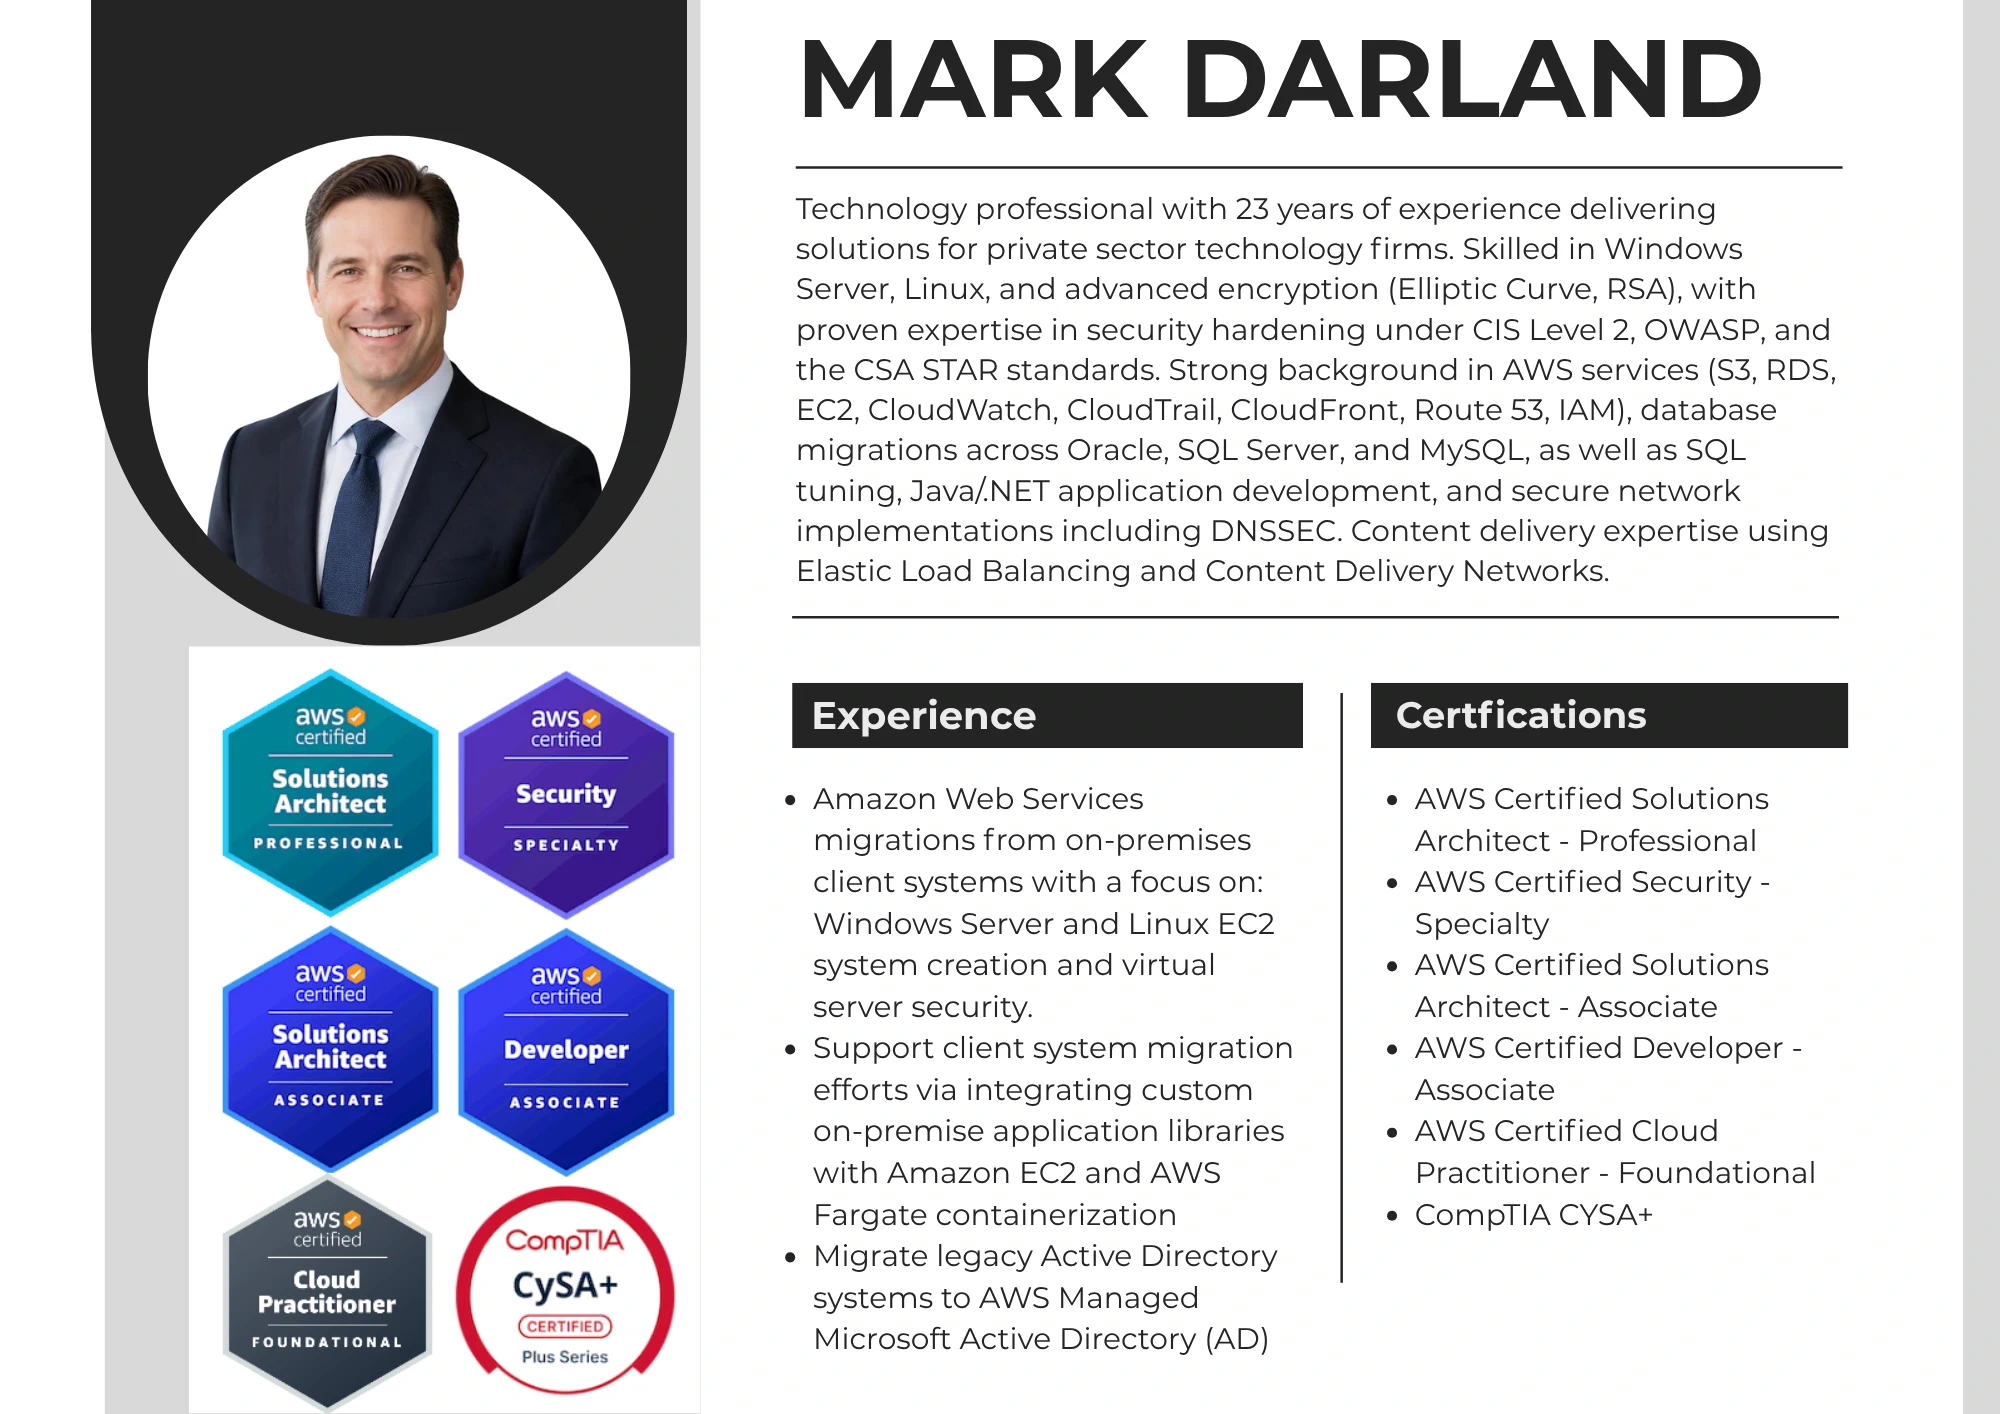
Professional Background
Throughout my career, I have worked with organizations ranging from small businesses to Fortune 500 enterprises, consistently delivering secure, scalable infrastructure solutions. My approach combines deep technical knowledge with practical implementation experience.
I have led numerous security hardening initiatives, ensuring systems meet industry standards including CIS Benchmarks, NIST frameworks, and PCI-DSS requirements. My work emphasizes both immediate security improvements and long-term architectural resilience.
Continuous learning is central to my practice. I stay current with emerging threats, security tools, and best practices, enabling me to provide forward-thinking solutions that protect critical assets.
Core Competencies
Linux Server Hardening
Expert configuration of SELinux, AppArmor, firewall rules, and kernel security parameters for enterprise-grade protection.
Windows Server Security
Comprehensive Group Policy configuration, PowerShell automation, and Windows Defender deployment across enterprise environments.
Cloud Infrastructure
Secure deployment and management of AWS and Azure resources with focus on IAM, network security, and compliance frameworks.
Network Security
Implementation of network segmentation, VPN solutions, intrusion detection systems, and security monitoring tools.
Additional Capabilities
- •Security auditing and vulnerability assessment
- •Patch management and system updates
- •Disaster recovery and business continuity planning
- •Configuration management with Ansible and Puppet
- •Container security (Docker, Kubernetes)
- •Log management and SIEM integration
- •Identity and access management (IAM)
- •Compliance documentation and reporting